Open to SOC Analyst & Incident Response roles

Hi, I'm Hassan Aldajah

> Cyber Security Eng & SOC Analyst

Fourth-year Cybersecurity student at the University of Jordan. Interested in SOC operations and digital forensics: detecting threats, analyzing network traffic and investigating incidents.

Hassan Aldajah
Case files & projects

Things I built, end to end.

Security tools, desktop apps and research. Each one is public, with real code behind it.

Nashmi logo
01 · AI SECURITY AGENT

Nashmi نشمي

An AI agent built exclusively for cybersecurity.

A SOC analyzer, CTF coach, security toolbox and practice exams in one app, with an Arabic and English interface.

  • Log Analysis (Linux / Windows) and Wireshark analysis (pcap, pcapng, CSV) that work without an API key
  • "+ Dashboard" with KPIs, timeline, ATT&CK chips and a 3D evidence graph
  • Google sign-in with two-step verification and per-user encrypted PostgreSQL storage
PythonStreamlitPostgreSQLOAuth 2.02FAThree.jsPlotly
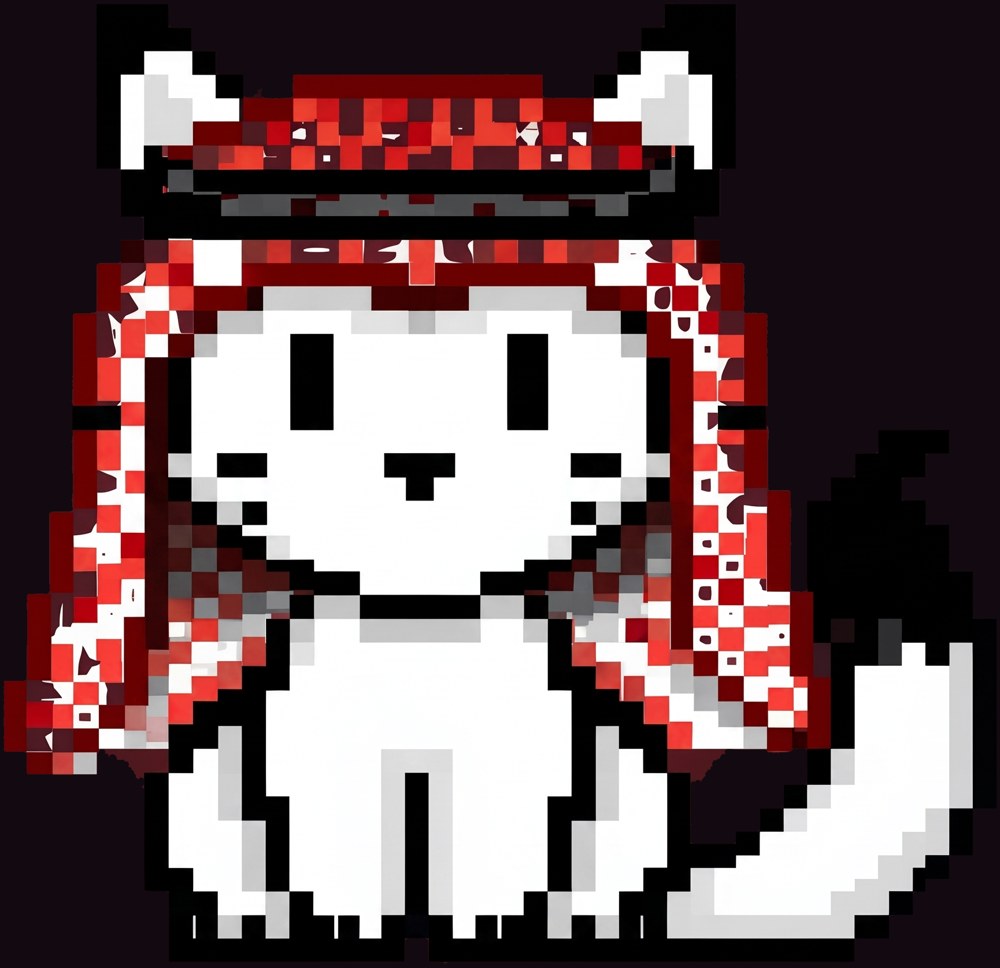
Nashmi, the pixel-art fox with the red shemagh
threat score 87events 12,480
nashmiagent.streamlit.app
02 · DESKTOP APP

Pixel image studio

A photo editor that treats every image as untrusted.

Local-first and offline: no accounts, no cloud, no telemetry. Every file passes a security gate before it is ever opened.

  • Security Gate: real-byte type check, YARA malware rules, hidden-payload scan, sandboxed decode, clean re-encode
  • GPU-accelerated WebGL 2 editor with non-destructive edits, curves, HSL, layers and masks
  • Pixel Art, object Eraser (PatchMatch), Retouch and Upscale, all with ordinary algorithms and no AI models
Tauri 2ReactTypeScriptWebGL 2FastAPIYARANumPy
pixels
security gate passedVirusTotal 0 / 69
pixels — Windows · Linux
The Pixels editor: tools, canvas and inspector
Safe Share logo
03 · GRADUATION PROJECT

Safe Share

End-to-end encrypted file sharing. Even admins can't read your files.

A zero-knowledge, AI-powered platform for sharing sensitive files, deployed on AWS and isolated behind JWT authentication.

  • End-to-end encryption (AES / RSA): files are encrypted on your device before they leave it
  • Client-side key generation: the keys never reach the server
  • Zero-knowledge architecture: no server-side access to your data
ReactSpring BootPostgreSQLAWSAES/RSAJWT
safeshare: Secure Media Network
safe-share-gold.vercel.app
FC logo
04 · FILE CONVERTER

FC File Converter

Every file tool, one glass octagon on your screen.

Drop files on it, or select them in File Explorer and press Ctrl+Alt+C. The octagon turns into the right tools for those files. Originals are never overwritten.

PythonPyQt6PyMuPDFPillowFFmpegGitHub Actions
FC logo
FC — Ctrl+Alt+C

Threat Eye SOC Detection

Threat-intelligence-driven SOC pipeline in Splunk Enterprise: 957,674+ network-flow events and a Random Forest classifier for AI-based correlation.

SplunkPythonscikit-learnREST API
Project report (PDF) ↗

MedCare Horizon Strategy

Security strategy for a 350-bed hospital: RBAC, IoT segmentation, a 5-goal enterprise plan and an ISO/IEC 27001 gap assessment.

Security StrategyISO/IEC 27001Risk Assessment
Case study (PDF) ↗
Toolbox

Tools & technology

Splunk
Autopsy
FTK Imager
Wireshark
IDA Pro

Soft skills

Analytical thinkingReport writingTeam collaborationCommunicationTime managementAdaptability
Experience

Practical experience

Hands-on Technical Training

JODBE · 40 hours of intensive technical training.

Credentials

Certifications

HTB Certified Defensive Security Analyst (CDSA)

Hack The Box · self-learning, SOC analyst path.

AWS Academy Graduate · Cloud Foundations

20 hours of comprehensive cloud foundation training.

AWS Academy Graduate · Cloud Security Foundations

20 hours of specialized cloud security training.

Cyber Warriors Competition Training

National Cyber Security Center (NCSC) · 25 hours.

Cybersecurity Practical Training with JODBE

40 hours of intensive technical training.

Contact

Let's talk.

Let's work on SOC & digital forensics together.